Introduction
A strong password doesn’t have to be a long string of random letters that you can never remember. In fact, trying to memorize dozens of complicated passwords often leads people to reuse the same password across several accounts.
That creates a much bigger security problem.
If one website suffers a data breach and your password is exposed, criminals may try the same email address and password combination on other websites. A unique password for every important account limits the damage when one account is compromised.
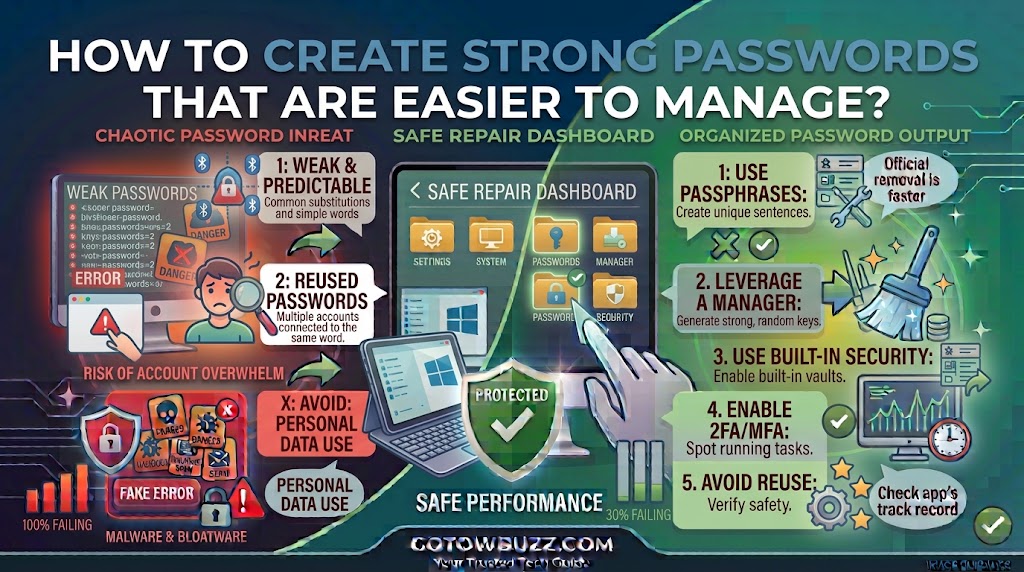
The practical solution is to stop thinking about passwords as something you must memorize individually. Use long, unique passwords or passphrases, let a reputable password manager remember them, turn on multi-factor authentication where available, and use passkeys when a service supports them.
This approach gives you stronger account protection without requiring you to keep a notebook full of passwords or repeatedly invent new ones.
Why Password Reuse Is Such a Problem
Imagine you use the same password for your email, shopping account, social media account, and an online service.
The password may be reasonably difficult to guess. But if one of those services is breached and the password is exposed, the attacker doesn’t necessarily stop there.
They can try the stolen credentials on other services.
This is why password uniqueness matters as much as password complexity.
The National Institute of Standards and Technology (NIST) recommends using passwords that are sufficiently long and notes that services should compare new passwords against lists of commonly used or compromised passwords. NIST also recommends allowing password managers and paste functions so users can create and manage stronger credentials.
A password that is unique to one account can’t be reused against another service if it is exposed.
What Makes a Password Strong?
Several factors affect password strength, but two practical ideas matter most for everyday users:
Length and uniqueness.
A longer password or passphrase generally gives an attacker more possibilities to work through, especially when it isn’t based on an obvious phrase or pattern.
For example, something like:
Summer2026
is short, predictable, and commonly structured.
A password such as:
river-lamp-copper-window-planet
is considerably longer and can be easier for a person to remember if you had to memorize it.
However, there’s an important distinction: don’t use that example as your actual password.
For accounts that support password managers, a randomly generated password is usually a better choice than creating your own predictable phrase.
Use a Different Password for Every Important Account
One of the simplest improvements you can make is to stop reusing passwords.
Your email account should have its own password.
Your banking account should have its own password.
Your shopping accounts should have their own passwords.
Your social media accounts should have their own passwords.
This might sound difficult if you have dozens of accounts. That’s exactly where a password manager becomes useful.
Instead of memorizing 30 different passwords, you only need to remember one strong master password for the password manager, while the manager stores the individual credentials.
NIST specifically recommends password managers because they make it easier for users to maintain distinct passwords for different services.
Let a Password Manager Generate Random Passwords
A password manager can generate passwords that are difficult to guess and store them securely so you don’t have to memorize them.
A generated password might look something like:
vN7!qL2#zR8@pX4$kM
You don’t need to remember it.
When you log into the website later, the password manager can fill it in for you.
This solves two problems at once: you get unique passwords, and you don’t have to invent them yourself.
Many modern browsers and operating systems also include password-management features. You don’t necessarily need a separate paid application just to begin using a password manager.
Step 1: Choose a password manager you trust
You can use a reputable standalone password manager or a password-management feature built into a browser or operating system you already use.
Before choosing one, check:
- Whether it supports your devices
- Whether it offers secure synchronization if you need it
- Whether it supports multi-factor authentication
- Whether you can export your stored passwords
- How account recovery works
- What security information the provider publishes
Don’t choose a password manager simply because an advertisement calls it the “most secure.”
Look at its actual features and security documentation.
[Screenshot 1: A reputable password manager interface showing a password vault with account entries]
Screenshot purpose: Show readers what a password manager looks like when storing separate login credentials. The screenshot should avoid displaying any real passwords, email addresses, recovery codes, or other private information.
Screenshot caption: A password manager keeps unique account passwords in one protected vault.
Create a Strong Master Password
If your password manager uses a master password, protect it carefully.
This is the password that can unlock your collection of stored credentials, so it deserves more attention than an ordinary website password.
A memorable passphrase can be a practical option.
For example, you could create a phrase made from several unrelated words rather than using a familiar quotation, name, birthday, or predictable sentence.
Don’t use a phrase from this article.
Don’t use your name combined with a year.
Don’t use your children’s names, pet names, favorite sports teams, or other information someone could learn from your social media accounts.
The goal is something long, difficult for another person to predict, and unique to the password manager.
If the password manager offers a secure recovery mechanism, understand how it works before relying on it.
Don’t Build Passwords Around Personal Information
A common mistake is taking something memorable and adding a few symbols.
For example:
Michael1990!
or
Pakistan@2026
may look more complicated than a basic word, but the underlying pattern is still predictable.
Avoid using:
- Your name
- Family members’ names
- Pet names
- Birth dates
- Phone numbers
- Addresses
- Favorite teams
- Company names
- Common phrases
- Simple keyboard patterns
Attackers can obtain surprisingly large amounts of personal information from public profiles, previous data breaches, and other sources.
Your password shouldn’t be a puzzle built from information about you.
Use Passphrases When You Need to Remember a Password
There are situations where you may need to remember a password rather than rely entirely on a password manager.
A long passphrase can be easier to remember than a short password filled with symbols.
For example, imagine a fictional phrase such as:
Cedar Window Bicycle Ocean Lantern
The words are unrelated, which makes the phrase less obvious than a familiar sentence.
Again, don’t use this exact example.
You can create your own passphrase using several unrelated words.
The important part is that it isn’t a famous quotation, song lyric, common saying, or predictable personal phrase.
For passwords generated and stored by a password manager, randomness is preferable because you don’t need to remember the result.
Don’t Follow Old Password Rules Just for the Sake of Complexity
You may have seen password requirements such as:
“At least eight characters, one uppercase letter, one lowercase letter, one number, and one symbol.”
Those rules can encourage people to create predictable patterns such as:
Password1!
Modern password guidance puts much more emphasis on length, uniqueness, and blocking commonly used or compromised passwords.
NIST’s current digital identity guidance recommends minimum password lengths of at least 15 characters for passwords used as a single authentication factor, while allowing shorter passwords in some situations where the password is used with another authentication factor. It also recommends allowing long passwords rather than imposing unnecessarily restrictive maximum lengths.
This doesn’t mean every website will follow the same requirements.
If a website has its own password rules, you’ll need to follow those rules.
Turn On Multi-Factor Authentication
A strong password is only one layer of account protection.
Multi-factor authentication (MFA) requires an additional verification step when you sign in.
For example, after entering your password, a service may ask you to approve a sign-in through an authenticator app or provide another verification factor.
This means someone who obtains your password may still be unable to access the account.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) strongly recommends using MFA and notes that it provides additional protection even when a password is compromised.
Step 2: Enable MFA on important accounts
Start with your most valuable accounts.
Check the account’s:
Settings > Security
or:
Account > Security
Look for terms such as:
Multi-factor authentication
Two-factor authentication
2FA
Sign-in verification
The exact menu depends on the service.
Follow its instructions to connect an authenticator app, security key, or another supported authentication method.
[Screenshot 2: An example account Security settings page showing a multi-factor authentication option]
Screenshot purpose: Show where users typically find MFA settings without exposing any real account information or security codes.
Screenshot caption: Add multi-factor authentication to important accounts for an additional layer of protection.
If you have to choose between receiving a one-time code by text message and using a stronger supported method such as an authenticator app or security key, check what the service supports and choose the stronger practical option available to you.
Consider Passkeys Instead of Passwords
Passkeys are becoming another useful way to sign in without typing a traditional password.
Instead of entering a password, a passkey can use the device’s built-in security features, such as a fingerprint, face recognition, PIN, or device unlock method.
The underlying cryptographic credentials are designed so that the private key stays on your device or in the credential system rather than being shared with the website in the same way a password is.
The FIDO Alliance describes passkeys as credentials designed to replace passwords and notes that they can provide phishing-resistant authentication.
Step 3: Look for a passkey option
When you’re signed in to an account, open its security settings.
Look for:
Passkeys
Sign in with a passkey
or a similar option.
If available, follow the service’s instructions to create one.
[Screenshot 3: An account security page showing a Passkeys section or Add Passkey option]
Screenshot purpose: Demonstrate where a reader might find passkey setup while making clear that the exact interface varies by service.
Screenshot caption: If an account supports passkeys, you may be able to sign in without entering a traditional password.
Don’t delete an existing password simply because you created a passkey unless you understand the account’s recovery and sign-in options.
Protect Your Email Account First
Your email account deserves special attention.
Why?
Because email is often connected to password resets for other accounts.
If someone gains access to your primary email account, they may be able to request password-reset links for other services.
For that reason, use a unique, strong password for your email account and enable MFA or a passkey if the provider supports it.
Then review the account’s recovery options.
Make sure the recovery email address and phone number, where used, are still yours.
[Screenshot 4: An email account security settings page showing password, MFA, and recovery options]
Screenshot purpose: Show the types of security controls readers should review on an important email account. The image should use a demonstration account with all personal details hidden.
Screenshot caption: Secure your main email account because it can be used to recover access to other accounts.
Store Recovery Codes Somewhere Safe
Some services provide backup or recovery codes when you enable MFA.
These codes can help you regain access if you lose your normal authentication method.
Treat them like sensitive credentials.
Don’t leave them in an open text file on your Desktop.
Don’t post them in a chat.
Don’t store a screenshot in an easily accessible photo folder without considering who could access it.
A password manager with secure notes may be appropriate if you trust its setup, or you can use another secure storage method recommended by the service.
Before changing phones or deleting an authenticator app, make sure you’ve understood the account’s recovery process.
[Screenshot 5: A fictional MFA setup screen showing recovery codes with the actual codes obscured or replaced with placeholders]
Screenshot purpose: Explain where recovery codes may appear during MFA setup without ever displaying usable authentication codes.
Screenshot caption: Save recovery codes securely when an account provides them.
Check Whether Your Password Has Been Compromised
Sometimes a password stops being safe because the service you used it on has suffered a breach.
That doesn’t necessarily mean your computer was hacked.
A company’s database may have been exposed, or credentials may have appeared in a breach.
If you learn that a service you use has suffered a breach, change the password for that account.
If you reused that password anywhere else, change those accounts too.
This is another reason unique passwords matter.
You don’t need to wait until something goes wrong to improve your passwords, either. Periodically review important accounts and replace passwords that have been exposed or reused.
Change Reused Passwords in the Right Order
If you’ve reused one password across many websites, don’t panic and try to change every account at once.
Start with the accounts that could cause the most damage if compromised.
A sensible order is:
- Primary email
- Financial and payment accounts
- Cloud storage
- Social media accounts
- Work or school accounts
- Shopping and other important services
Create a new unique password for each one.
Then save it in your password manager.
If an account supports MFA or a passkey, enable that too.
This gives you a manageable process instead of a huge password-cleanup project.
Don’t Share Passwords Through Normal Messages
Avoid sending passwords through ordinary email, text messages, or chat whenever possible.
A message can be forwarded, copied, synchronized to another device, or remain in a history that you later forget about.
If you need to give someone access to a service, check whether the service supports delegated access, family sharing, account members, or another safer sharing feature.
Some password managers also provide controlled credential sharing.
The best option depends on the service and the reason another person needs access.
Be Careful With Saved Passwords on Shared Computers
Saving passwords can be convenient on your personal computer.
On a shared or public computer, it can create a serious privacy problem.
Don’t allow a browser to save your passwords on a computer that other people can access.
Don’t leave your password manager unlocked when you’re away from your computer.
On your own PC, use Windows security features such as a strong sign-in method and lock the computer when you leave it unattended.
Press:
Windows + L
to lock Windows quickly.
This doesn’t replace account security, but it prevents someone physically using your unlocked computer while you’re away.
What to Do If You Think a Password Has Been Stolen
Act quickly, but don’t panic.
Start by changing the password for the affected account.
If you reused that password elsewhere, change those accounts too.
Then enable MFA or a passkey if available.
Review recent account activity for unfamiliar sign-ins, devices, or changes.
Check whether the account’s recovery email address or phone number has been changed.
If you see unauthorized activity, follow the service’s official account-recovery and security instructions.
Don’t use links from suspicious emails to change the password. Instead, open the service’s official website or app yourself.
This reduces the risk of being sent to a phishing page.
Common Password Mistakes to Avoid
Using one password everywhere
This creates a single point of failure.
Making tiny changes to the same password
Changing Password2026! to Password2027! doesn’t create a genuinely independent password.
Using personal information
Names, birthdays, teams, and other personal details can be easier to guess than people expect.
Saving passwords in an unprotected text file
A file called MyPasswords.txt is not a suitable password-management system.
Sharing passwords through chat
Normal messaging isn’t designed to be a secure credential vault.
Ignoring MFA
A strong password plus another authentication factor is generally better than a password alone.
Using the same recovery information everywhere
Keep your account recovery details current and understand how each important account can be recovered.
Installing unknown password-management software
Use established providers or built-in password-management features from platforms you trust. Avoid downloading software from random websites.
A Simple Password System for Everyday Use
If you’re starting from scratch, you don’t need to change everything in one day.
Use this simple process.
Step 1: Secure your email account
Give it a unique password.
Enable MFA or a passkey if available.
Check recovery options.
Step 2: Choose a password manager
Pick a reputable option that works across the devices you actually use.
Step 3: Change reused passwords
Start with financial, email, cloud, work, and other important accounts.
Step 4: Generate new passwords
Let the password manager create random passwords instead of inventing them yourself.
Step 5: Turn on MFA
Enable it for important accounts wherever it is available.
Step 6: Add passkeys where appropriate
If a service offers passkeys, consider using one as an alternative to traditional password sign-in.
Step 7: Save recovery information securely
Store recovery codes and other emergency information somewhere protected.
Step 8: Stop creating new passwords manually
Once your system is working, let the password manager generate and save new passwords whenever you create an account.
This is much easier to maintain than trying to memorize increasingly complicated passwords.
Frequently Asked Questions
How long should a strong password be?
Longer is generally better. Current NIST guidance says passwords used as a single authentication factor should be at least 15 characters, while allowing longer passwords is recommended. Individual websites may impose different requirements.
Is a password manager safe to use?
A reputable password manager can make account security easier because it allows you to use unique passwords without memorizing all of them. Choose a provider carefully, protect the password manager account with strong authentication, and understand its recovery options.
Should I use the same password for all my accounts?
No. Every important account should have a unique password. If one password is exposed, unique passwords prevent that credential from automatically becoming useful against your other accounts.
Are passphrases better than passwords?
A long, unpredictable passphrase can be easier to remember than a short complex password. For accounts managed by a password manager, randomly generated passwords are often more practical because you don’t need to memorize them.
Should I change my passwords regularly?
You don’t necessarily need to change a strong password on a fixed schedule when there is no indication it has been compromised. Change it when you know or suspect it has been exposed, when you’ve reused it across accounts, or when the service tells you there has been a security incident. NIST’s current guidance also advises against requiring arbitrary periodic password changes without evidence of compromise.
Is two-factor authentication worth using if I already have a strong password?
Yes. MFA adds another layer of protection if someone obtains your password. CISA recommends MFA because it can protect accounts even when passwords are compromised.
What should I do if I forget my password manager’s master password?
Use the provider’s official recovery process if one is available. Don’t rely on guesses or random websites offering to recover the password. Before storing important credentials in a password manager, understand what happens if you lose access to the vault.
Final Thoughts
Creating strong passwords becomes much easier when you stop trying to memorize every password yourself.
Use a unique password for each important account, make passwords long and unpredictable, and let a reputable password manager generate and store them. Protect your main email account especially carefully, enable MFA where possible, and consider passkeys when they’re offered.
The biggest improvement isn’t making one incredibly complicated password. It’s making sure that one stolen password can’t unlock several parts of your digital life.
Start with your email account today, then work through your most important accounts one by one. Once the system is in place, new accounts become much easier to manage.
Sources Used for Accuracy
- NIST — Digital Identity Guidelines: Authentication and Authenticator Management (SP 800-63B) — used for current guidance on password length, password managers, compromised-password screening, password changes, and password requirements.
- CISA — More than a Password: Multi-Factor Authentication — used for guidance on MFA and additional account protection.
- FIDO Alliance — Passkeys — used for the explanation of passkeys and their authentication model.